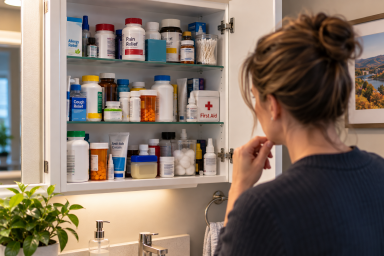
Take a look inside the average medicine cabinet and you'll probably find quite a collection.
- Cold medicine from last winter.
- Vitamins someone bought and forgot about.
- A couple of half-empty bottles.
- Maybe something that's been sitting there long enough that nobody remembers why they bought it.
There's plenty of medicine.
But nobody would look at a full medicine cabinet and say: "We must be really healthy."
Cybersecurity can work the same way.
Over the years, businesses accumulate security tools.
- Your insurance company requires something.
- A new threat leads to another purchase.
- A software vendor recommends something else.
- A compliance requirement adds another layer.
Individually, every decision may have made perfect sense. But eventually, it's worth asking:
What do we actually have, why do we have it, and is everything working together the way it should?
Because having more cybersecurity products isn't necessarily the same as having better cybersecurity. More Tools Don't Automatically Mean Better Protection
It's an understandable assumption.
If one security product makes the business safer, adding another should make it even safer. And sometimes it does.
There are good reasons to have multiple layers of protection. If one layer misses something, another may catch it. But those layers should be there on purpose.
Over time, businesses can end up with overlapping tools, old services nobody is quite sure they still need, or protections that were added to solve a problem that no longer exists. At the same time, there may be something important that's missing.
That's why we don't think the goal should be: "How many cybersecurity products do we have?"
A much better question is: "Do we have the right protections for the way our business operates today?"
Think of Cybersecurity as a System
Your immune system isn't one thing. It's a collection of different defenses working together. Cybersecurity should operate in much the same way.
Your business may have email filtering, endpoint protection, multifactor authentication, backups, security awareness training and monitoring.
But those pieces shouldn't operate as unrelated products. Someone needs to understand how they fit together. Someone needs to know when something isn't working. Employees need to understand what's expected of them. And there needs to be a clear process for what happens when something unusual occurs.
That's the difference between owning security tools and having a cybersecurity strategy.
Give Your Cybersecurity a Checkup
You don't need to understand every technical detail of every cybersecurity product your company uses. That's what your IT provider is there for.
But as a business owner or leader, you should be able to get understandable answers to a few basic questions.
- What are we using, and why?
Ask your IT provider to explain the major security protections your business has. Not in acronyms. Not in technical specifications. In plain English.
What does this do for our business, and why do we need it?
There should be a reasonable answer. If you're paying for something and nobody can explain what purpose it serves, that's worth investigating.
- Where do things overlap—and where are the gaps?
Overlap isn't necessarily bad. In cybersecurity, some overlap is intentional. Multiple layers can provide additional protection.
But there's a difference between intentional layers and three products doing essentially the same thing because nobody realized all three were still there. Your IT provider should be able to explain the difference.
And while you're looking at overlap, ask the opposite question: Is there anything important we're assuming is protected that actually isn't?
That's often the more useful conversation.
- Who's Actually Paying Attention?
This is a big one.
Security software can generate alerts all day long. But an alert isn't particularly useful if nobody sees it. Who reviews those alerts? What happens when something important is detected? Who determines whether action needs to be taken? How quickly does that happen?
You don't necessarily need to know the technical process behind every alert. You should know that someone is responsible for the outcome.
A security tool isn't a strategy simply because it's installed.
- Does Our Cybersecurity Still Fit Our Business?
Businesses change. You hire employees. People leave. You add locations. Employees start working differently. You adopt new software. Your insurance requirements change. Your industry requirements may change.
The cybersecurity approach that made perfect sense three years ago may not perfectly match the business you're running today. That's why cybersecurity shouldn't be something you set up once and forget.
Periodically, it's worth asking: "If we were designing our cybersecurity around our business today, would we do anything differently?"
You may discover everything still makes sense. That's a perfectly good outcome.
Or you may find a few things worth changing. That's useful too.
The Goal Isn't More Cybersecurity. It's the Right Cybersecurity.
This is where I think the medicine-cabinet analogy really matters. If we review your cybersecurity and determine that you genuinely need another layer of protection, we'll tell you why.
But adding another product shouldn't automatically be the answer.
- Sometimes the better solution is configuring something you already have correctly.
- Sometimes it's eliminating unnecessary overlap.
- Sometimes it's improving a process.
- Sometimes it's employee training.
- Sometimes it's making sure someone is actually monitoring the tools you've already invested in.
And sometimes, yes, another safeguard makes sense. The important thing is understanding why.
That's what a coordinated cybersecurity approach looks like.
Let's Have the Conversation
Most business owners don't want to become cybersecurity experts. They just want to know that the right protections are in place, they're being managed properly, and someone is paying attention.
That's a reasonable expectation.
At Literati IT, we help businesses throughout Morgantown, Fairmont, Clarksburg and North Central West Virginia step back and look at the whole picture—what you already have, what each piece is doing, whether there are unnecessary overlaps, and whether there are areas that deserve more attention.
If it's been a while since anyone has explained your cybersecurity to you in plain English, let's have that conversation.
Call us at 304-296-8026 or visit www.literatiit.com to schedule a quick discovery call.
No pressure. No scare tactics. No technical jargon. Just a practical conversation about whether the cybersecurity you're paying for is the cybersecurity your business actually needs.